TypeSafe's X Account Got Phished on Launch Day. Here's How to Protect Yours.
San Francisco lab TypeSafe spent two years in stealth building AI for software. Hours after launch, its X account was hacked. The team got it back that night.
On September 15, 2026, TypeSafe AI came out of stealth with a $40 million seed round led by DCVC. Its first model, Jev, is what the company calls a System One model: instead of writing text, it returns typed decisions that software can use directly.
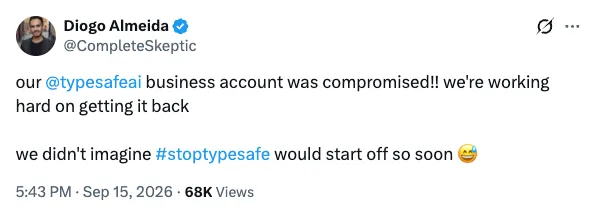
Hours after the launch, TypeSafe’s X account, @typesafeai, was phished. Here’s how the day unfolded (times in PT):
- 11:17am Launch announcement
- 5:43pm CEO Diogo Almeida reports the compromise
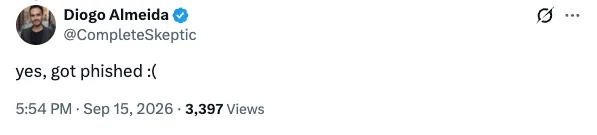
- 5:54pm Almeida names phishing as the cause
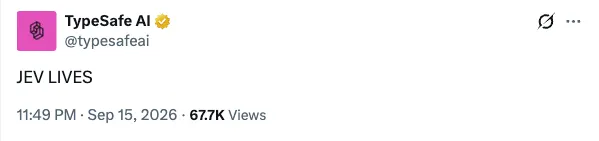
- 11:49pm Account regained: “JEV LIVES”
Almeida broke the news that evening.
Replying to a follower 11 minutes later, he said the cause was phishing.
Before midnight, the team had the account back.
TypeSafe hasn’t said how the account was phished, but it handled the response well. Moving fast and in public helped limit the risk of misinformation or malicious links spreading from the compromised account.
The attack also landed on launch day, a known social-engineering window when teams are stretched thin and inboxes fill up, so a phishing message is easy to miss.
How to protect your X account on launch day
These steps are written for X, but they apply to any company social account.
- Lock the account down before you announce. Turn on two-factor authentication with a passkey or hardware security key rather than SMS codes.
- Shrink the list of people who can log in. Remove old contractors and agencies. Where the platform supports it, give teammates their own delegated access instead of sharing one password.
- Never sign in from a link. Launch day brings press requests, partnership pitches and urgent-looking platform notices. If a message asks you to log in, go to x.com directly.
- Verify requests on a second channel. If anyone asks for a code or password, or asks you to post on the company’s behalf, confirm it with them over a call or a separate app first.
- Plan the recovery before you need it. Make sure the recovery email and phone belong to the company, not one person. Keep another account ready to warn followers, the way TypeSafe’s CEO did.
About Common Defense
Common Defense is an AI cyber lab built by security veterans and AI researchers, whose team has helped protect more than $300B in assets across 1,100+ security engagements. We help AI companies, fintechs, and crypto protocols secure the communication channels and operations that attackers target most.