Skip to content
Blog

The channels attackers actually use

Field notes from Common Defense on social engineering, communication-channel attacks, and the defenses we build to stop them.

One defense. Every channel. The Common Defense communication firewall.
Social Engineering··3 min read

The Communication Firewall is Live

Scammers now reach people on every channel they use for work: email, voice, text, WhatsApp, and Telegram. Nearly every major breach starts the same way, with a message or call that looks legitimate on a channel the company already trusts. Here's how it happens, and what we built to stop it.

Read article →
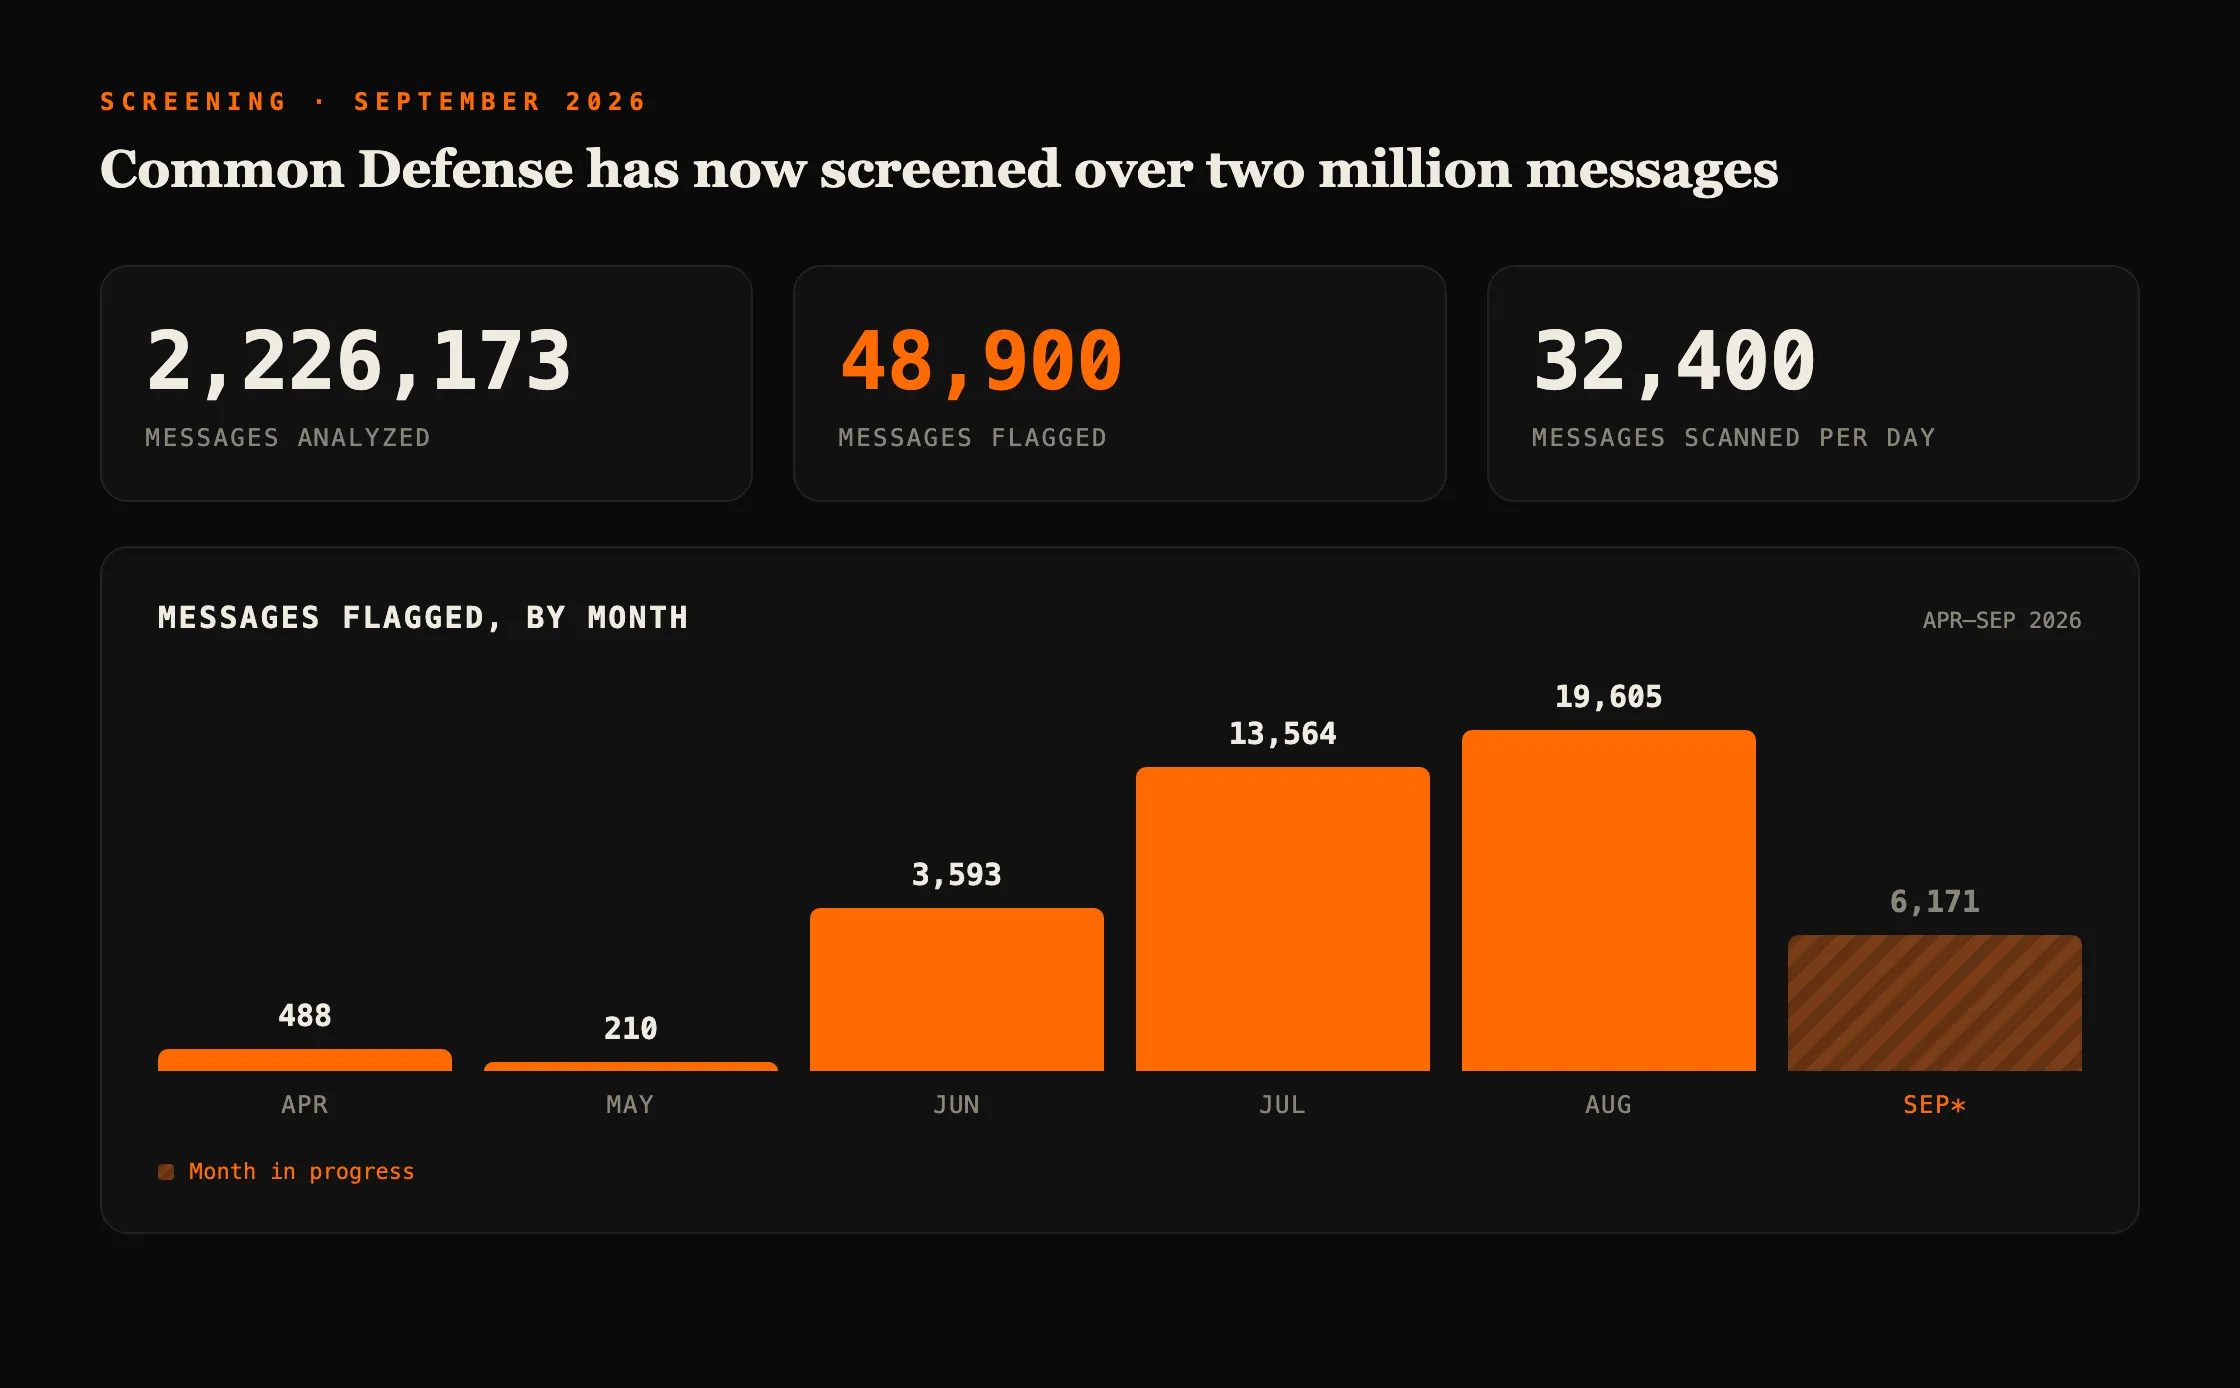
Three totals: messages screened, messages flagged, messages scanned per day, above a bar chart of messages flagged each month, April through September 2026.
Product·

Common Defense Has Now Screened Over Two Million Messages

2 million scanned messages and 48,900 threats detected, and the monthly count shows the growth curve behind the total, not just the milestone.

Fraudulent remote employment. They did not break in. They got hired.
Research·

The Hiring Funnel Is Now an Insider-Threat Surface

Huntress investigated five suspected DPRK remote workers in 2026, at healthcare and financial-services employers, in sales and medical roles as well as IT. Fraudulent remote employment is an identity-and-access problem that starts at hiring, and the evidence to catch it sits in systems that do not share a queue.

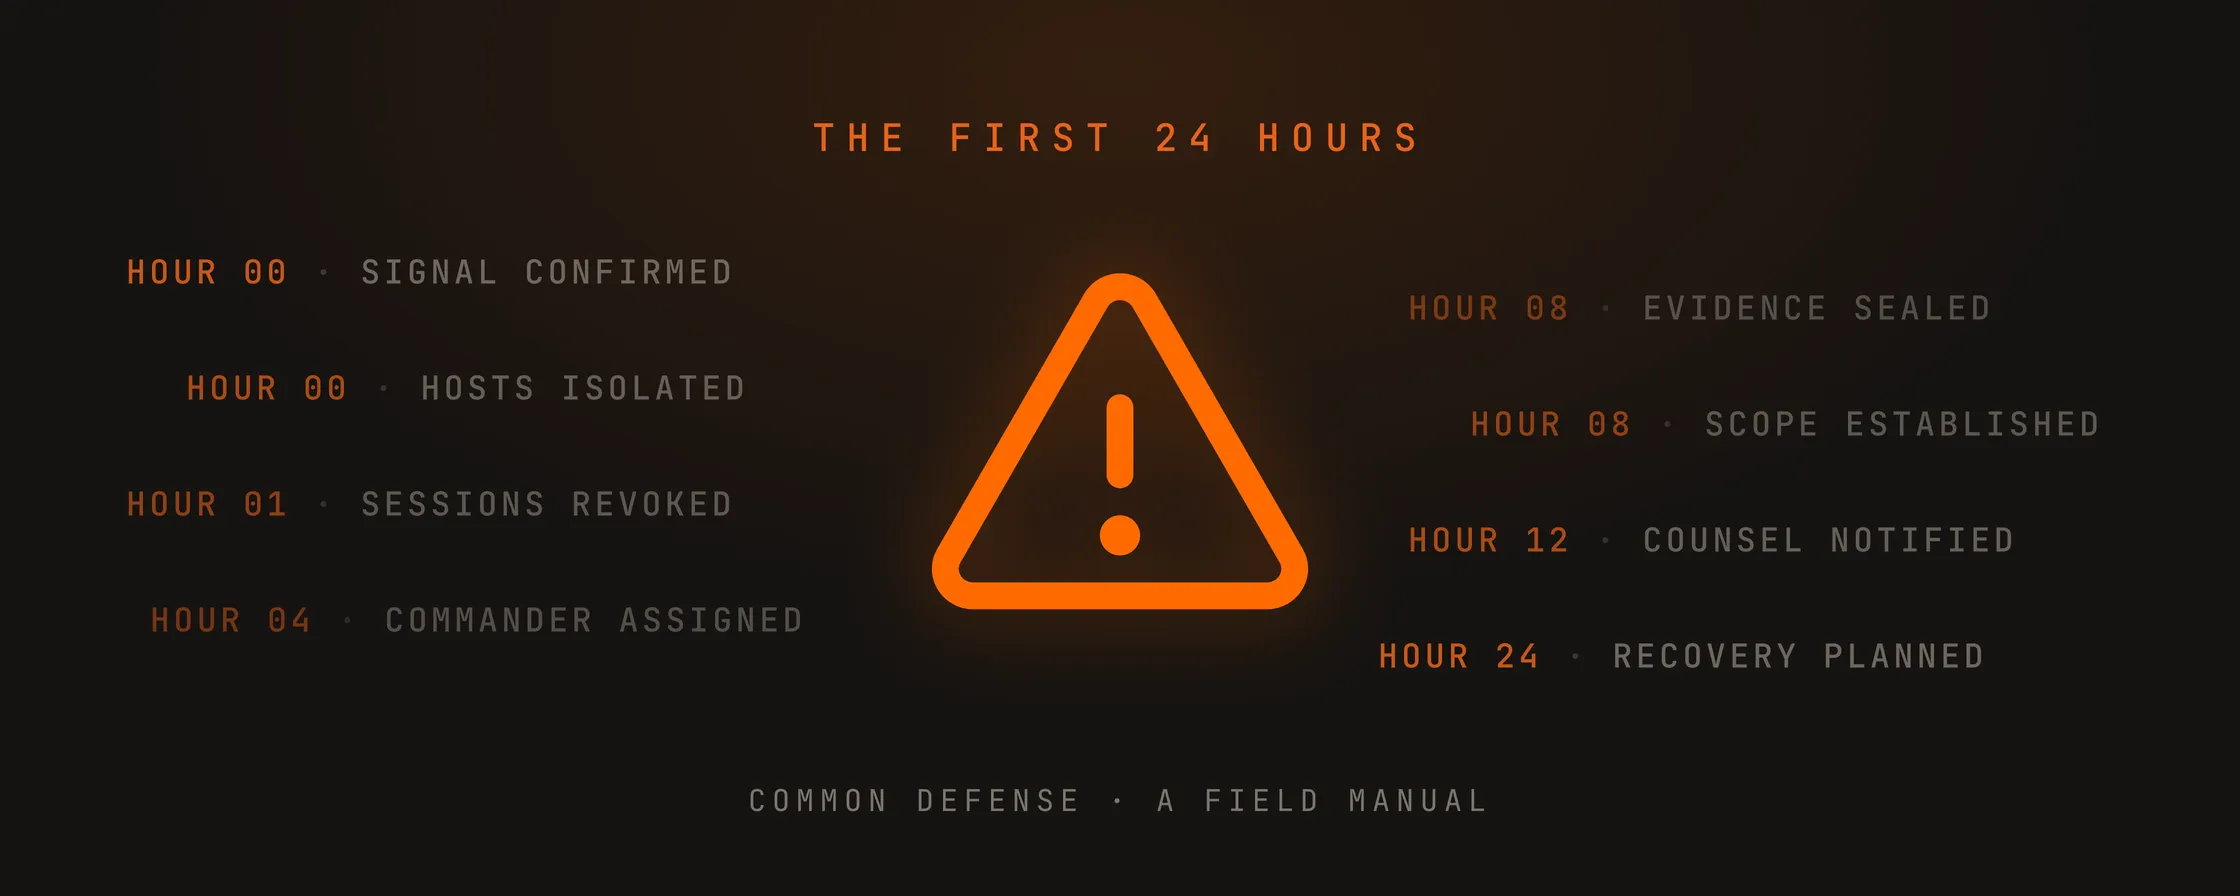
The first 24 hours. A warning symbol at the centre of an incident timeline running from hour 00, signal confirmed and hosts isolated, through hour 24, recovery planned.
Incident Response·

Your Company Was Hacked. Here's Exactly What to Do in the First 24 Hours.

A step-by-step incident response guide for the first 24 hours: contain the breach, preserve evidence, communicate without panic, and recover. Includes the AI-native threat angle most playbooks miss.

Incident analysis. The device never went online. The Bitcoin left anyway.
Key & Signer Compromise·

The Coldcard Hack

The safest place to keep Bitcoin was supposed to be a device that never touches the internet. Over five days, attackers drained more than $100M from those devices without physically touching a single one. Here's what went wrong, and why it started five years before anyone lost a coin.

Operational security. The audit covers the code; the operation around it (identity, code supply chain, external services, devices) goes unaudited.
Operational Security·

The Audit Passed. The Operation Didn't.

Application security asks whether the code is correct. For most of the last three years, the losses answered a different question.

March 2026. The Axios Hack. The Common Defense read on the axios npm compromise.
Supply Chain·

The Axios Hack

In March 2026, attackers took over the npm account behind axios, a JavaScript library that's pulled around 100 million times a week. Every step looked legitimate, right up until a prompt in a meeting asked the maintainer to install an update. Here's how it happened.